certrally


certrally is a command line client for certificate enrollment with the Certificate Management Protocol (CMP), Enrollment over Secure Transport (EST) and the Simple Certificate Enrolment Protocol (SCEP). It is free software under the Apache License 2.0.
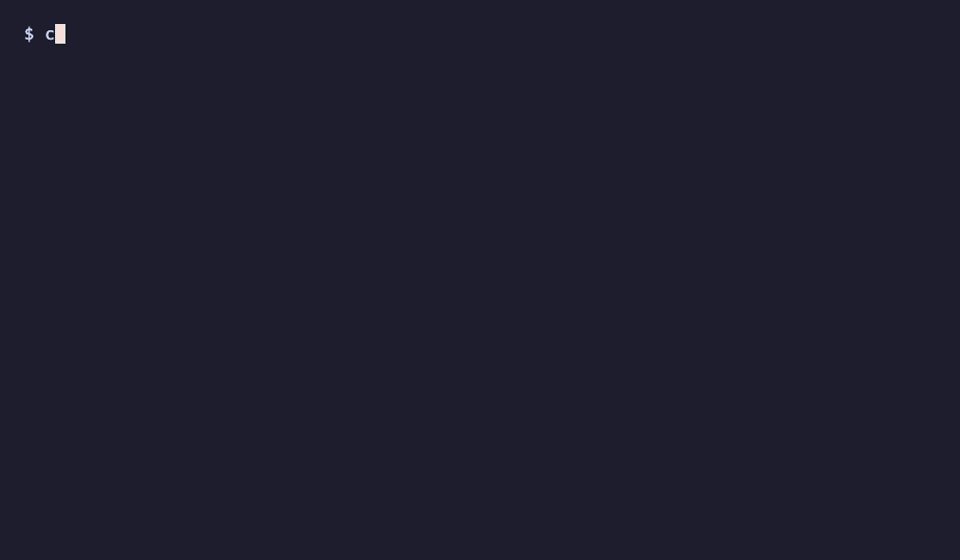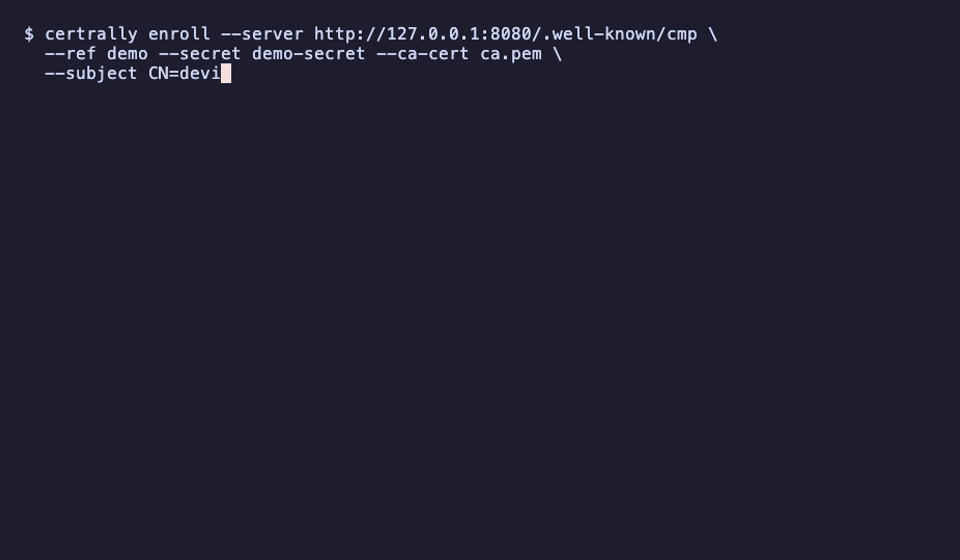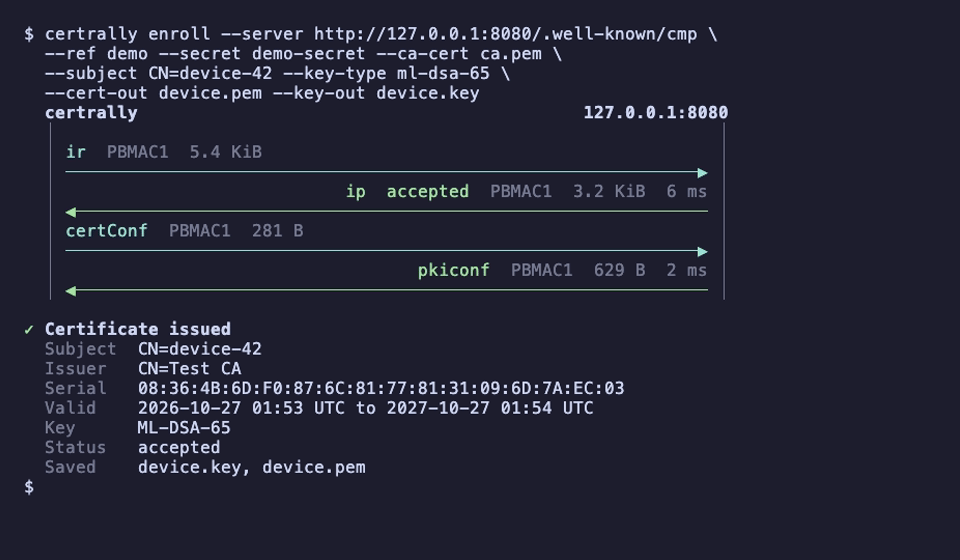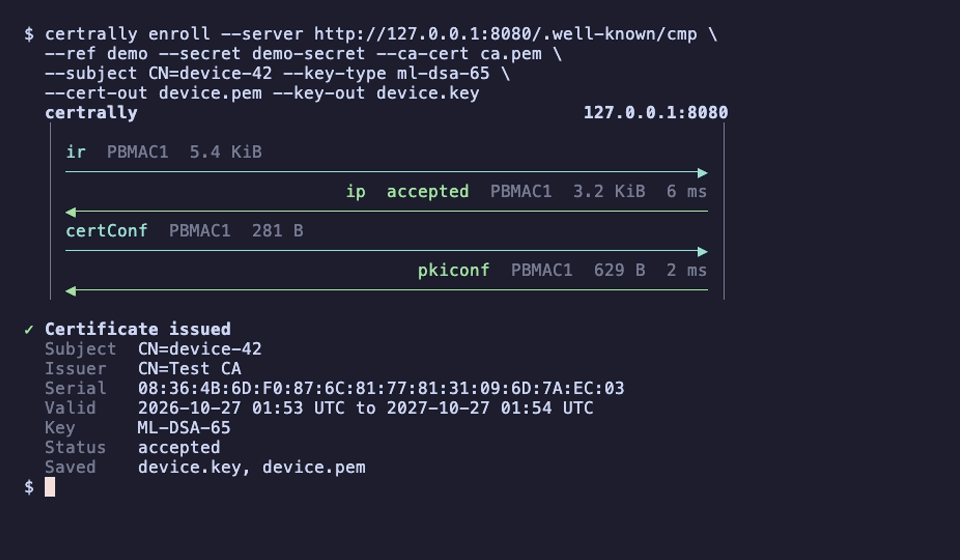
CMP (RFC 9810, which replaces RFC 4210, with the RFC 9483 profile)
ir,cr,kur,p10crandrrwith a shared secret or a certificate- Keys that the CA generates (central key generation)
- Requests forwarded by a registration authority in nested messages
- CA certificates, root CA updates, request templates and CRLs from the CA
pingto check a server andmockto run a test CA on your machine- Deliberately wrong messages with
enroll --faultto test how a CA copes - A step-by-step
enrollthat prints the matching command for scripts
EST (RFC 7030)
- Enrollment, renewal, server key generation, CA certificates and CSR attributes
- Authentication with a password, a bearer token, a TLS client certificate or TLS-SRP
est mockto run a test EST CA on your machine
SCEP (RFC 8894)
- Enrollment, renewal and polling of pending requests, also in a later run
- CA certificates, the CA chain, the next CA certificate, certificates and CRLs from the CA
- Digest, cipher and HTTP method chosen from the server capabilities, with old algorithms on request
scep mockto run a test SCEP CA on your machine
All protocols
- A live diagram of every message and plain explanations of failures
- RSA, ECDSA, Ed25519, ML-DSA, composite ML-DSA and ML-KEM keys, also offline with
keygen. SCEP takes RSA and ECDSA keys - No trust setup: certrally trusts the CA it talks to or the one in
--ca-cert - Warnings about responses that break the RFCs and a strict profile that rejects them
- JSON output, capture files and exit statuses for scripts
inspectandlintto decode recorded messages and check them
Tested with EJBCA, Nokia NCM, Insta Certifier and the openssl cmp mock server over CMP, with Cisco libest over EST and with EJBCA, Nokia NCM, OpenXPKI and micromdm/scep over SCEP. Tested servers lists how each one behaves.
Where to go next
| I want to | Page |
|---|---|
| Install certrally | Install |
| Pick a protocol and try a test CA | Getting started |
| Enroll, renew and revoke over CMP | Using CMP |
| Enroll and renew over EST | Using EST |
| Enroll and renew over SCEP | Using SCEP |
| Choose key types, encrypted keys or DER output | Keys and output files |
| Run certrally from a script | Scripts and exit status |
| Check responses against the RFCs | RFC checks |
| Decode and check recorded messages | Inspect and lint recorded messages |
| Run a test CA on my machine | CMP test CA, EST test CA and SCEP test CA |
| Test how a CA copes with wrong messages | Testing a CA with faulty messages |
| Find notes for my CA server | Tested servers |
| Check a download | Verify a download |
| Ask for help or report a problem | Support |
| Contribute | Contributing |